Security and privacy
Your credentials, your RBAC, your machine.
kdashboard is a desktop app that reads the API server directly. There is no backend of ours between you and your cluster, because there is no backend of ours.
Your kubeconfig stays put
Contexts are read from the files you already have. Credentials are never copied, uploaded or cached anywhere else.RBAC is the ceiling
Every list, every action and every namespace in the picker is what your user may do. A forbidden call surfaces as a forbidden call.Loopback only
The only HTTP listeners on your host are the agent MCP endpoints on 127.0.0.1, behind a token. One lives only while an agent session runs; the other is opt-in. Everything that leaves your machine Five rows · there is no sixth
DestinationWhenWhatCan you turn it off?
Your Kubernetes API server all the time the same calls kubectl would make that is the product
Your Prometheus only if you configure one range queries for usage history leave it blank
Your container registry only when trivy or grype scans image manifests, from the local scanner do not install a scanner
GitHub releases · pricing data first open of Cost or Rightsizing, then daily a rate table download, no cluster data do not open those views
GitHub releases · update feed once at startup a version number request no
No analytics, no crash reporting, no accounts, no licence server, no “anonymous usage statistics” — not even an opt-in one.
How the window is built The renderer is sandboxed and never touches Node or Electron APIs directly. One IPC channel through a preload contextBridge, plus event channels for streams. Agent tools re-enter the same dispatcher the UI uses — they cannot reach further than you can. The four mutating tools block on an in-app Approve or Deny.
Where we are not there yet Stated here rather than left for you to discover on first launch.
macOS signingad-hoc, not notarized
macOS in-place updatesoff, use Homebrew
Linux · Windows updateselectron-updater
Reporting something
Please do not open a public issue for a vulnerability. The security policy in the repository
has the address and what to include; we answer and credit reporters.
And it helps you with your own security
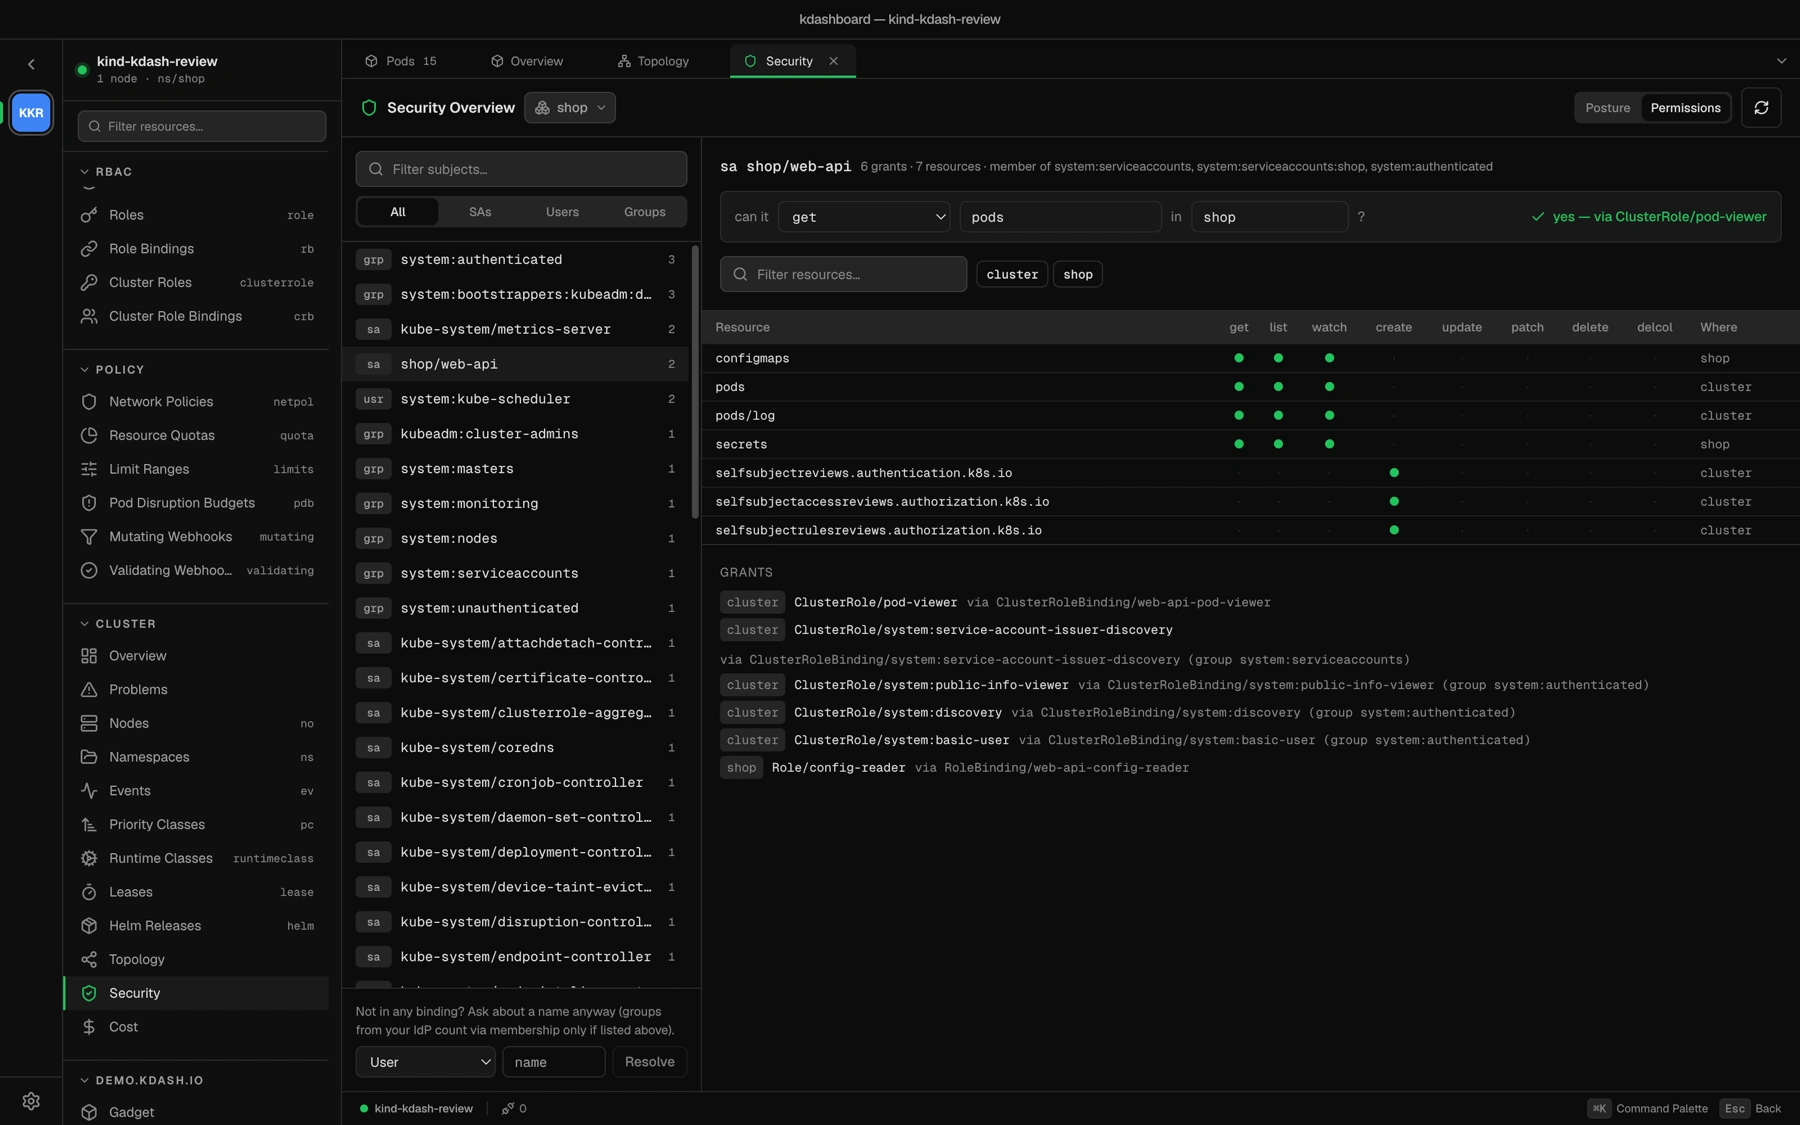
Who can do what, answered in one screen.
The permissions explorer resolves a subject across every Role, ClusterRole and group, prints the verb matrix, and answers the direct question: can this ServiceAccount get deployments in this namespace? Image vulnerabilities come from a trivy or grype you install yourself. Read the Security and RBAC guide →
verb matrix can it … ? missing roles cluster-admin flag trivy · grype